Role-Based Access & Audit Trails for Multi-Branch Operations
Who can see and change what is not an IT detail. It is how a distributed operation prevents fraud and proves control.
Lakshay
Assistant Vice President · Brand Systems & Conversion Craft
Four rights, not one
View controls visibility, edit covers creation and change, delete is a rare destructive right, and approve remains separate wherever money or compliance is involved. The maker should not automatically be the checker.
Roles that mirror the organisation
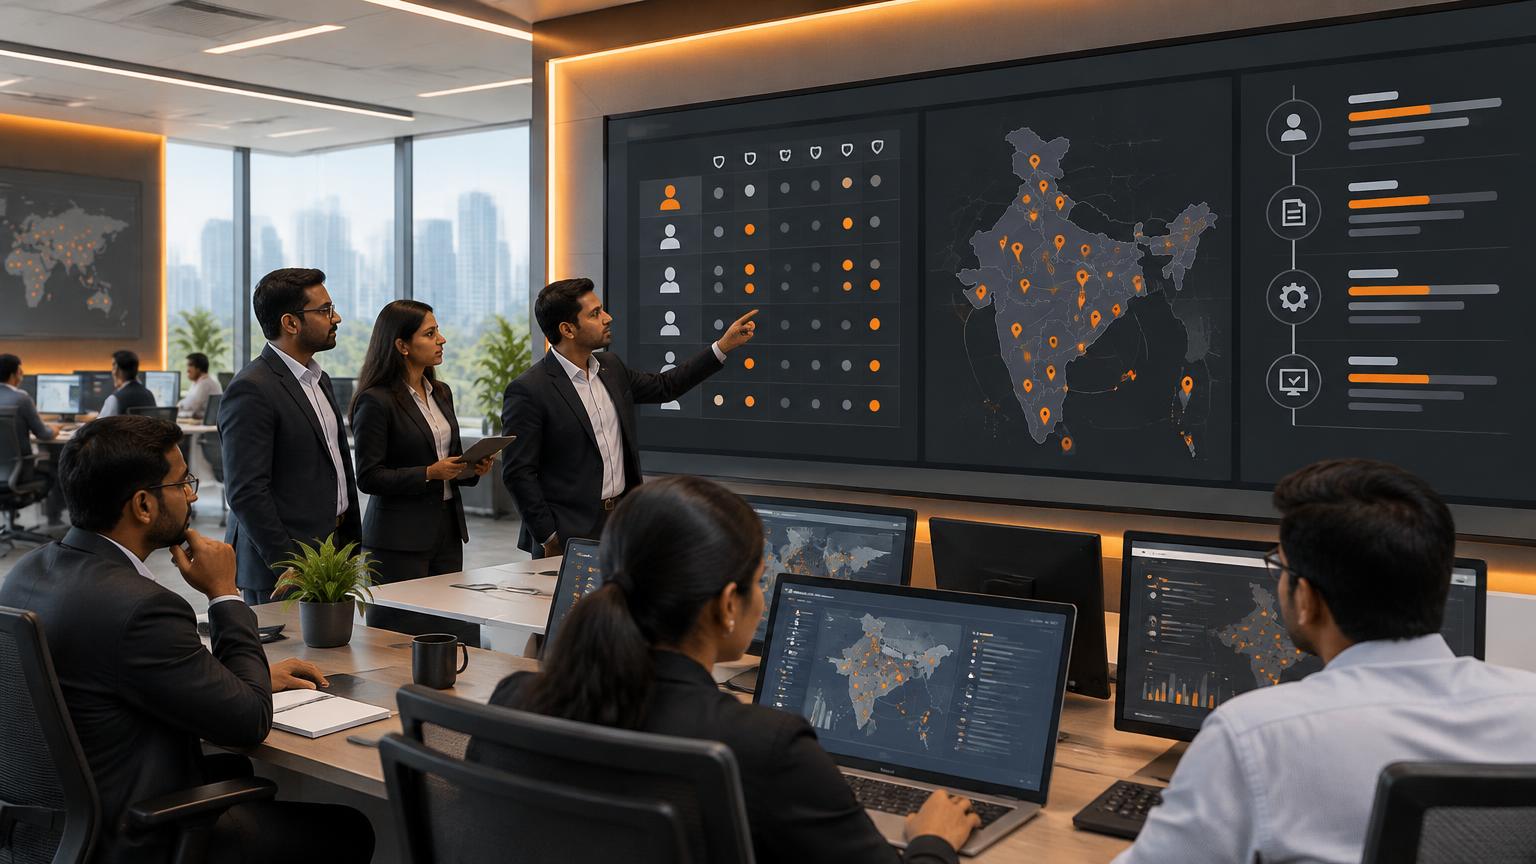
Guards see their own attendance and records. Field officers see mapped sites and teams. HR, Finance and Control Center receive the modules they operate. Branch managers see their branch, while leadership sees cross-branch dashboards and approvals.
Rights and scope are different
Rights define what an employee can do; scope defines which records. A Pune manager should not see Chennai payroll, and a field officer should only see mapped sites. Scope must be enforced where the data is queried, not merely by hiding menu items.
Three layers of control
The screen hides unavailable actions, the server rechecks every request, and row-level database rules constrain every query to the authenticated user’s scope. The final layer protects data even if a screen or request is manipulated.
The audit trail
Record actor, module, record, action and timestamp for every sensitive create, update, enable, disable and delete. Keep before-and-after values for rate, payroll, contract and offboarding changes, and make the log append-only and exportable.
Five rules for safer access
Limit approve rights to genuine signatories, make delete rare, change roles immediately when jobs change, review permissions quarterly with HR and Finance, and never share logins.
Topics & keywords
- role based access control
- audit trail software
- multi branch access control
- row level security
- Hyper Ops
Key Takeaways
- Separate approval from edit rights.
- Enforce branch and site scope at the data layer.
- Preserve append-only evidence of sensitive changes.
Frequently asked
Can an agency create its own roles?
Yes. Roles can mirror the organisation, with permissions set per module and approval kept separate.
Is an application audit log fully tamper-proof?
It can be append-only in the application; stronger assurance adds protected backups and independent retention controls.