Absconding Guards & Rehire Fraud: Building a Do-Not-Rehire Workflow
Close the gaps that let kit disappear, ghost pay continue and a poor exit return as a fresh employee record.
Priti Rohatgi
Board of Director · Strategy & Ecosystem Architecture
Where exits leak money
An incomplete exit leaves uniforms and ID cards unreturned, allows an absent person to remain on the muster roll and lets a terminated employee rejoin through another branch as a new candidate. One connected exit process closes all three gaps.
Record the exit properly
Capture exit type, offboarding date, last working day, statutory update dates, reason, rating, future-hiring review and every item still held by the employee. Login and future deployment should follow the recorded status.
Recover before closure
Create a collection task for the field officer, record what was returned and require a reason for missing items. Upload relevant exit and ID evidence before making the employee fully inactive.
Catch a rejoin at the door
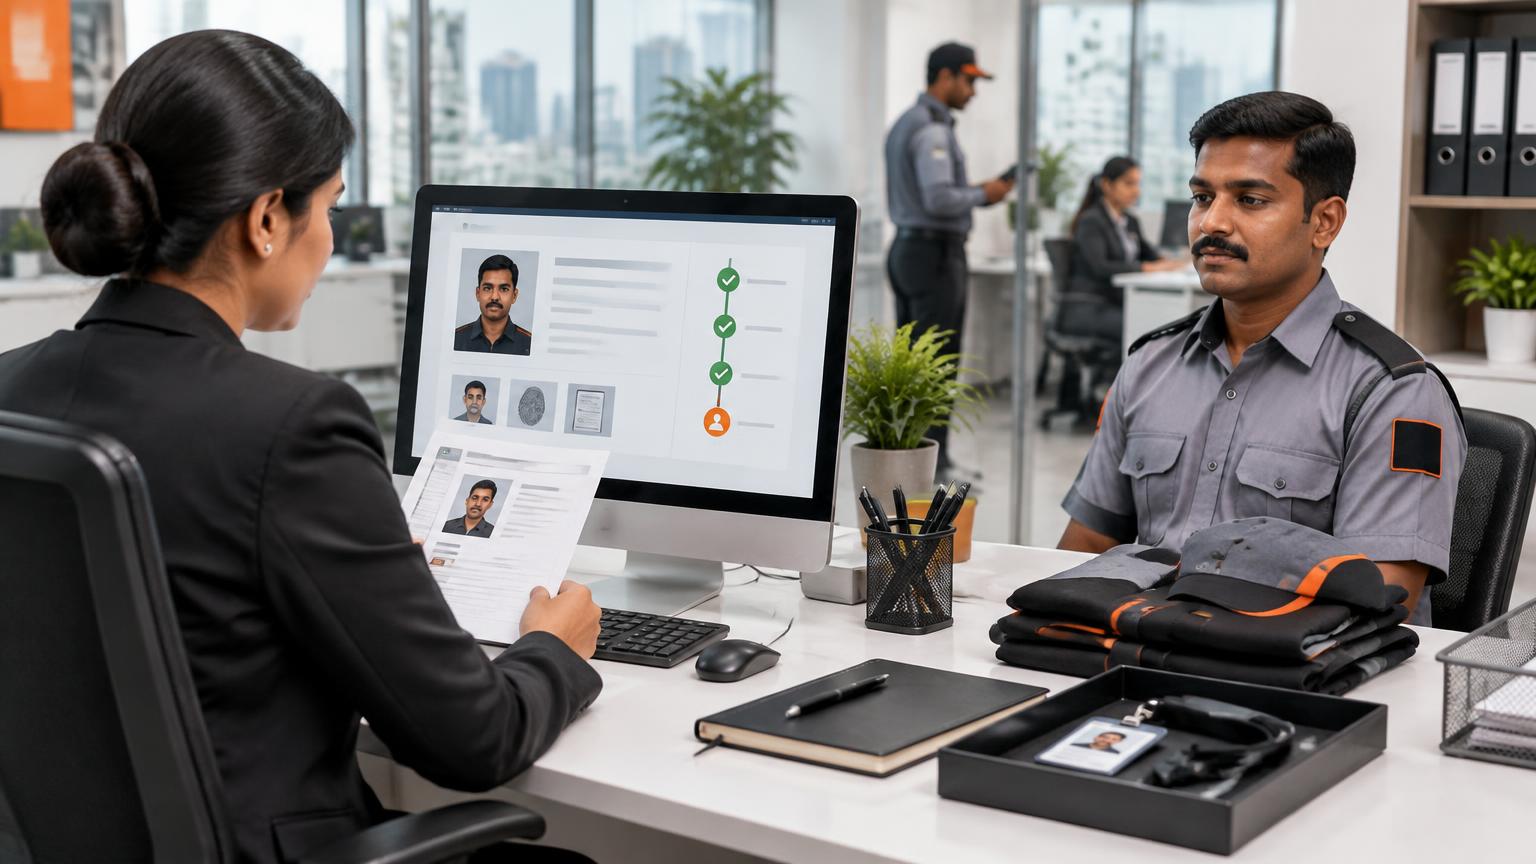
Identity duplicate detection should stop a new employee record and surface the existing history. Operations and leadership can review the previous exit, rating and do-not-rehire status before authorised HR reactivates the original record.
Keep the process humane
Not every no-show is deliberate absconding. Illness and emergencies happen. Record facts, contact the employee and family contact according to policy, and allow authorised review to change a flag with a reason while preserving history.
Topics & keywords
- absconding employee process
- do not rehire list
- employee offboarding security agency
- rehire fraud
- Hyper Ops
Key Takeaways
- Treat offboarding as an operational workflow, not a status switch.
- Link recovery tasks to the employee exit.
- Use identity matching to prevent silent duplicate hiring.
Frequently asked
Can a do-not-rehire flag be removed?
An authorised reviewer can change it with a recorded reason; the previous history should remain visible.
What if a returning guard has a new mobile number?
Identity matching should use a stable verified identity rather than the mobile number alone.